Before You Connect: A Researcher's Quiet Experiment in Airport and Café Wi-Fi Exposure
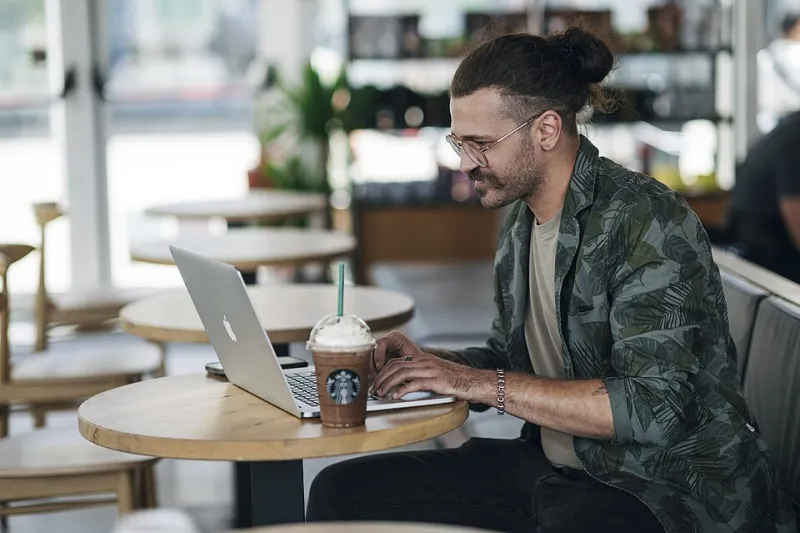
Photo: Shixart1985, CC BY 2.0, via Wikimedia Commons
The first surprise came eleven minutes into a layover at Denver International Airport, before any login screen appeared. A researcher running a passive traffic monitor on their own laptop had already broadcast the device's previous network history — a list of network names the machine was searching for — to anyone in the terminal with inexpensive software and the patience to look.
That experiment, repeated over three weeks at airports in Denver and Atlanta, hotel lobbies in Chicago, and coffee shops in Seattle and Austin, forms the basis of this report. The methodology was deliberately conservative: no networks were attacked, no other users were monitored, and nothing was done that would run afoul of the Computer Fraud and Abuse Act. The goal was simply to answer a question most travelers never think to ask — what does a laptop say about its owner before a single password is typed?
What Devices Announce Without Being Asked
Modern operating systems are talkative by design. When a laptop wakes from sleep, it sends out probe requests asking whether familiar networks are nearby. In the airport tests, those requests revealed fragments of the researcher's recent life: hotel network names from prior trips, a corporate network, a home network labeled with a street address.
Security researchers have documented this behavior for more than a decade, and major platform vendors have quietly responded. Modern mobile devices randomize their hardware identifiers and use abbreviated probe behavior. Laptops running current versions of Windows and macOS are considerably quieter than they were five years ago. But older machines, corporate laptops with legacy configuration profiles, and Internet of Things devices still leak freely.
The second exposure came after connecting. On the café's captive portal — the interstitial page requiring an email address or room number — the researcher's device began transmitting DNS lookups in plaintext. Email provider names, a news site, a cloud storage service: not the content of communications, but a legible outline of the morning's activities.
Where the Real Risk Lives
The conventional wisdom about public Wi-Fi — that a hacker in the corner is reading your email over your shoulder at the network level — has aged poorly. Two developments changed the calculus.
First, encryption became the default. The overwhelming majority of web traffic in the United States now travels over HTTPS, and major messaging platforms apply end-to-end encryption regardless of network. A hostile actor intercepting traffic sees encrypted streams, not messages.
Second, cellular connectivity became ubiquitous. The researcher's phone-hotspot tests showed that for most everyday tasks, tethering to a phone eliminates the shared-network threat model entirely.
What remains genuinely risky is narrower and more specific. Captive portals themselves are a threat: a laptop can be presented with a counterfeit portal, and users conditioned to click "Accept" do so reflexively. Login pages for sensitive accounts remain a hazard on untrusted networks — not because the password crosses the air in plaintext, but because a convincing phishing page served over the portal can harvest credentials before encryption ever begins. And plaintext protocols still in use by some enterprise tools, file-transfer utilities, and older email configurations remain visible to anyone monitoring the network.
The Theater Problem
The most interesting finding was what travelers worried about versus what they did. In informal conversations at airport gates — a decidedly unscientific sample, but a telling one — nearly everyone asked mentioned VPNs. Almost none mentioned checking that a banking site's certificate was valid, keeping operating systems patched, or reviewing what their device broadcast automatically.
A virtual private network remains a reasonable tool, particularly for people who must use untrusted networks regularly. But it has become a talisman. The researcher's own traffic analysis showed that with modern HTTPS defaults, the marginal protection a VPN added for casual browsing was modest — while the device's automatic announcements and the user's own susceptibility to a fake portal went entirely unaddressed.
Security theater thrives on this inversion: visible, purchasable protections substitute for the unglamorous habits that actually reduce risk.
A Practical Checklist for the American Traveler
The experiment suggests a short, legal, low-effort protocol:
- Treat the captive portal as hostile territory. Never enter credentials for any account while one is active. Wait until fully connected, or use a phone hotspot.
- Turn off automatic network connection. Prevent the device from broadcasting a list of remembered networks and from joining spoofed hotspots named after familiar places.
- Verify before you authenticate. Check that sensitive sites show valid certificates. Browser warnings on café Wi-Fi deserve attention, not dismissal.
- Prefer your phone's hotspot for anything sensitive. It removes the shared network from the equation at negligible cost on most US carrier plans.
- Update before you travel. Patched devices resist the attacks that untrusted networks make easier.
None of this requires specialized knowledge or recurring subscriptions. It requires only accepting that the device speaks before its owner does — and teaching it a little discretion.